
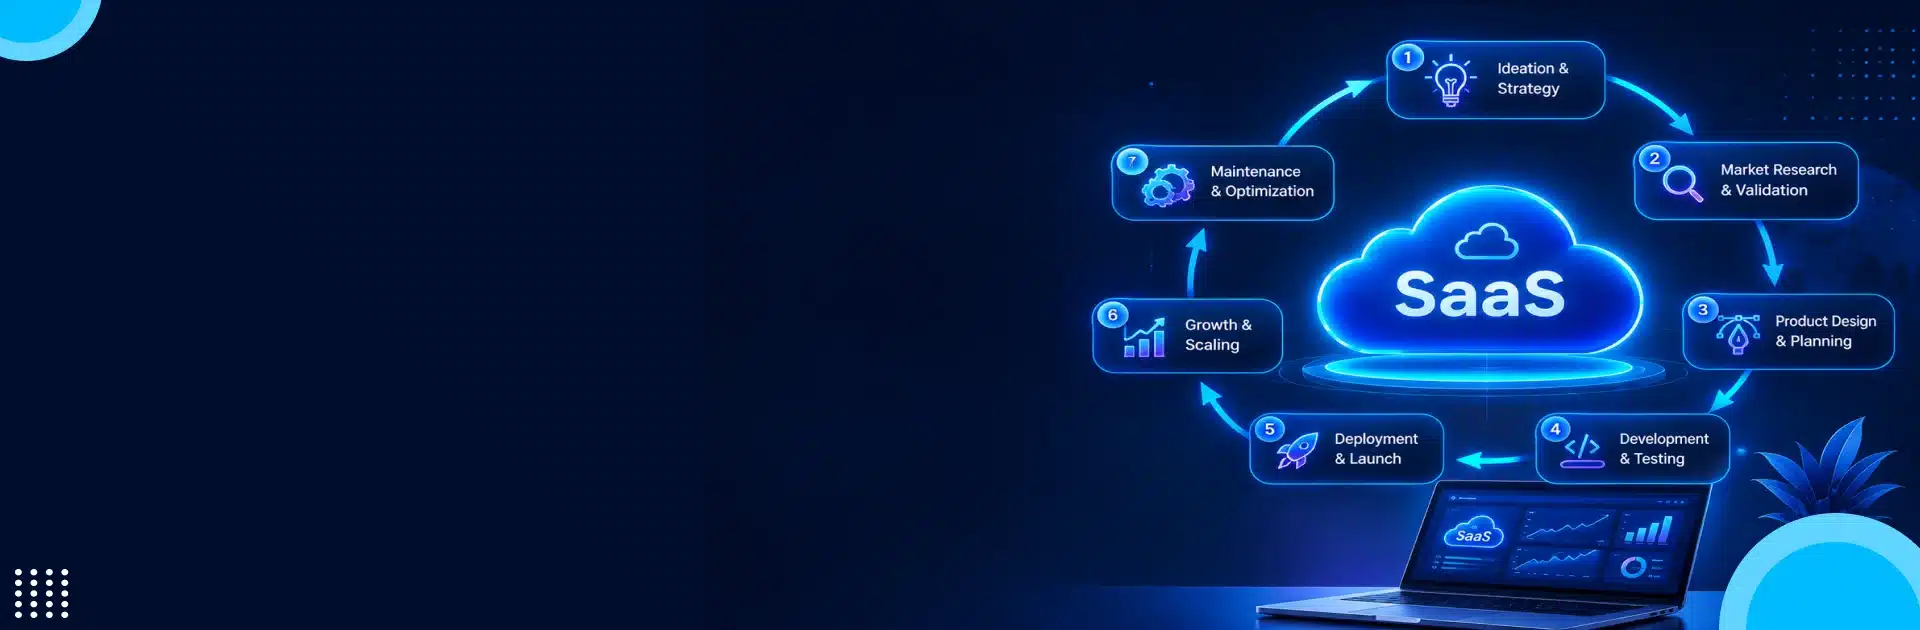
Key Takeaways
- The SaaS development lifecycle has 9 stages: discovery, requirements & planning, architecture, UI/UX design, development, testing & QA, deployment, operations, and continuous iteration.
- It’s a loop, not a line — stage 9 feeds back into stage 2, which is why SaaS products never reach a “final” release the way traditional software does.
- Architecture and compliance decisions (tenancy model, cloud provider, HIPAA/SOC 2/PCI-DSS scope) made in stages 2–3 are the hardest and most expensive to reverse later — get these right before development starts.
- Discovery is the most commonly skipped stage, and skipping it is the most common reason SaaS products don’t gain traction after launch.
- A typical MVP takes 4–8 months from discovery to launch, longer for compliance-heavy products in healthcare or fintech.
- This differs from the traditional SDLC mainly in ownership and cadence: the same team usually builds and operates the product, shipping continuously rather than in versioned releases.
The SaaS development lifecycle is the end-to-end process of building, launching, and maintaining a cloud-hosted software product — from initial discovery through continuous post-launch iteration. It has nine core stages: discovery and market validation, requirements and planning, architecture and technical planning, UI/UX design, development, testing and QA, deployment and launch, operations and maintenance, and continuous iteration.
Unlike traditional software, which ships once and is done, a SaaS product never reaches a final “finished” state. The last stage of the lifecycle feeds directly back into the first—usage data and customer feedback become the input for the next planning cycle. That loop, more than any individual stage, is what distinguishes SaaS development from a standard build-and-ship SDLC.
Ready to Build Your SaaS Product?
Get a technical assessment of your architecture, compliance scope, and timeline before you write a single line of code.
Quick reference: all 9 stages
| Stage | What it produces | Typical duration |
| Discovery & Market Validation | Problem definition, target ICP, competitive analysis | 2–4 weeks |
| Requirements & Planning | MVP scope, feature backlog, compliance requirements, roadmap | 2–3 weeks |
| Architecture & Technical Planning | Tenancy model, cloud provider, tech stack, API design | 2–4 weeks |
| UI/UX Design | Wireframes, prototypes, onboarding flows | 3–5 weeks |
| Development | Working application, built in sprints | 8–20+ weeks |
| Testing & QA | Verified, secure, load-tested build | Continuous, alongside development |
| Deployment & Launch | Live production release, billing integration | 1–2 weeks |
| Operations & Maintenance | Uptime, monitoring, support | Ongoing |
| Continuous Iteration | New features, retention improvements | Ongoing, in 2-week cycles |
9 Stages of the SaaS Development Lifecycle

1. Discovery & Market Validation
Before any design or code work starts, the goal is to confirm the problem is real and worth building for.
This stage answers three questions: Who is the product for? What are they doing today instead of using it? Will they pay for it? Skipping this — or rushing it — is the single most common reason SaaS products fail to gain traction after launch, regardless of how well they’re built.
What happens here:
- Problem and ICP (ideal customer profile) definition
- Competitive and market analysis
- Build-vs-buy assessment — is a custom SaaS product actually the right solution, or does an existing tool solve this cheaper?
- Early pricing model hypothesis (subscription tiers, usage-based, seat-based)
Deliverable: a validated problem statement and a rough product thesis, not a finished spec.
2. Requirements & Planning
This is where the MVP gets scoped and the project’s non-negotiables get written down — including compliance requirements, which need to be decided now, not discovered later.
What happens here:
- MVP feature list, prioritized by impact vs. effort — see our guide to MVP software development for how to scope this without over- or under-building
- Compliance and regulatory scope defined upfront: HIPAA for healthcare data (our HIPAA-compliant app development guide covers this in depth), PCI-DSS for payment handling, SOC 2 for enterprise buyers, GDPR for EU users. These requirements shape the architecture in stage 3 — they are not a checklist to bolt on after development.
- Roadmap and release plan (what ships in v1 vs. later phases)
- Team structure and sprint cadence
Why this matters more in SaaS than traditional software: a SaaS product is sold continuously, often self-serve, to customers who will churn if trust or compliance gaps surface post-signup. Getting this wrong is expensive to fix later — much of it is architectural, not cosmetic.
3. Architecture & Technical Planning
The decisions made here are the ones that are hardest — and most expensive — to reverse after launch.
Core decisions:
| Decision | Options | Why it’s hard to change later |
| Tenancy model | Multi-tenant vs. single-tenant | Multi-tenant is standard for most SaaS today; retrofitting it after building single-tenant means re-architecting the data layer |
| Cloud provider | AWS, GCP, Azure | Vendor lock-in through managed services increases over time |
| Data architecture | Shared database, siloed schemas, siloed databases | Affects both cost-to-scale and how compliance boundaries (e.g., HIPAA data isolation) get enforced |
| API design | REST, GraphQL | Determines how integrations and future mobile/partner access get built |
| Security baseline | Encryption at rest/in transit, IAM, audit logging | Retrofitting security controls after launch is a common source of enterprise-deal delays |
Deliverable: a technical architecture document that engineering, security, and compliance stakeholders have all signed off on — this becomes the reference point for every sprint that follows.
4. UI/UX Design
SaaS products are frequently adopted without a sales conversation — the interface has to do the selling. This makes UX a functional requirement, not a visual polish step.
What happens here:
- User flow mapping, especially the self-serve signup-to-value path (time-to-first-value is a tracked metric for most SaaS teams)
- Wireframes and interactive prototypes
- Design system setup — critical for a product that will ship new features every two weeks without becoming visually inconsistent
- Usability testing with real target users before development starts
5. Development
Development is the longest stage, and it’s where the architecture and design decisions from earlier stages get executed — not where they get decided.
What happens here:
- Agile, sprint-based execution — typically two-week sprints with defined deliverables and retrospectives
- Frontend, backend, and API build-out in parallel
- CI/CD pipeline set up from the start, not added later — this is what makes the “continuous iteration” stage possible post-launch
- Feature flagging, so incomplete features can be merged safely without being exposed to users
A note on scope: teams that skip stages 1–3 tend to discover their architecture can’t support a required feature midway through development. That’s the expensive version of this stage. Teams that do the earlier stages properly mostly spend this stage building, not re-deciding.
6. Testing & QA
Testing runs alongside development, not after it — but it intensifies before each release.
What gets tested:
- Unit and integration testing, ideally automated and run on every commit
- Load and performance testing — SaaS products need to perform predictably as tenant count grows, not just at demo scale
- Security testing, including penetration testing — frequently a hard requirement for enterprise, healthcare, and fintech buyers before they’ll sign a contract
- Multi-tenant isolation testing — confirming one tenant’s data and load can’t affect another’s
7. Deployment & Launch
What happens here:
- Production deployment, typically via blue-green or canary release patterns to avoid downtime for existing subscribers — this matters in SaaS specifically because there usually are existing subscribers by the time any given release ships
- Subscription billing and payment integration go live
- Onboarding flows and in-app guidance activated for new signups
- Monitoring and alerting configured before, not after, go-live
8. Operations & Maintenance
Once live, the responsibility shifts to keeping the product running reliably while customers depend on it.
What happens here:
- Uptime monitoring against SLA commitments
- Incident response and bug fixing
- Infrastructure scaling as usage grows
- Customer support and success workflows
9. Continuous Iteration
This is the stage that has no traditional SDLC equivalent, and it’s the one most generic explanations of “the SaaS lifecycle” underplay.
What happens here:
- Usage analytics and product data inform what gets built next
- Churn and retention analysis
- Feature releases on an ongoing cadence — not a single “version 2” launch
- Feedback loops from support and sales feed back into stage 2 (requirements & planning) for the next cycle
This is the loop that makes SaaS development a cycle rather than a straight line: stage 9 doesn’t end the process; it restarts stage 2.
Not Sure Where to Start?
We’ll help you scope your MVP, pick the right tenancy model, and map out compliance requirements — no commitment required.
SaaS Development Lifecycle vs. Traditional SDLC
| Traditional SDLC | SaaS Development Lifecycle | |
| End state | Shipped, versioned release | No final state — continuous delivery |
| Deployment | Periodic, often infrequent | Frequent, often weekly or biweekly |
| Ownership post-launch | Often handed to a separate maintenance team | Same team typically owns build and operate |
| Tenancy | Not applicable | Multi-tenant architecture usually required |
| Compliance | Scoped once at spec stage | Ongoing — subscription and data-handling requirements evolve with each customer segment |
| Success metric | On-time, on-spec delivery | Retention, churn, time-to-value |
Conclusion
The SaaS development lifecycle isn’t a straight line from idea to launch — it’s a loop, and the stage most teams underinvest in is usually the one that determines whether the product succeeds.
Two patterns are worth repeating, because they’re where most SaaS projects actually go wrong:
The expensive mistakes happen early, not late. Tenancy model, cloud provider, data architecture, and compliance scope — all decided in stages 2 and 3, before a line of application code is written — are the hardest and most costly decisions to reverse once development is underway. A multi-tenant retrofit or a bolted-on HIPAA control after launch costs far more than getting it right the first time. Teams that treat these as “we’ll figure it out later” decisions are the ones that end up rebuilding six months post-launch.
The lifecycle doesn’t end at launch — that’s roughly the halfway point. Stages 8 and 9, operations and continuous iteration, run for the entire life of the product and are where most of the actual engineering effort ends up going over time. A SaaS product that stops iterating after launch behaves like shipped software, which defeats the reason to build it as SaaS in the first place.
For teams building in regulated spaces — healthcare, fintech, or any product handling sensitive user data — this sequencing matters even more, since compliance requirements aren’t a documentation task at the end; they’re architectural decisions made in stages 2 and 3 that shape everything that follows.
FAQs
How many stages are in the SaaS development lifecycle?
Most frameworks describe six to nine stages. This guide uses nine: discovery, requirements and planning, architecture, UI/UX design, development, testing, deployment, operations, and continuous iteration. Shorter frameworks typically combine several of these into fewer named steps, but the underlying work is the same.
What’s the difference between the SaaS development lifecycle and the traditional software development lifecycle (SDLC)?
Traditional SDLC ends at deployment. The SaaS lifecycle treats deployment as one stage among several, with operations and continuous iteration feeding back into planning indefinitely — there’s no final release.
How long does the SaaS development lifecycle take?
For an MVP, 4–8 months from discovery through initial launch is typical, depending on compliance scope and product complexity. Compliance-heavy products (healthcare, fintech) generally run longer at the architecture and testing stages specifically.
Do all SaaS products need multi-tenant architecture?
No, but most do. Single-tenant is sometimes chosen for enterprise or highly regulated customers who require full data isolation, at the cost of higher infrastructure overhead per customer.
What’s the most commonly skipped stage?
Discovery and validation. It’s the easiest stage to compress under time pressure, and the most expensive one to have skipped once a product is built and not adopted.

Rishi Ram is CTO at GMTA Software, with 6+ years of experience in software architecture and technical leadership. He’s led GMTA’s work across fintech—including eWallet apps, mobile banking platforms, and Sharia-compliant fintech builds—as well as on-demand and taxi app development and AI-integrated products like fraud detection agents and workflow automation tools.